MiroTalk RND Self-Hosting Guide
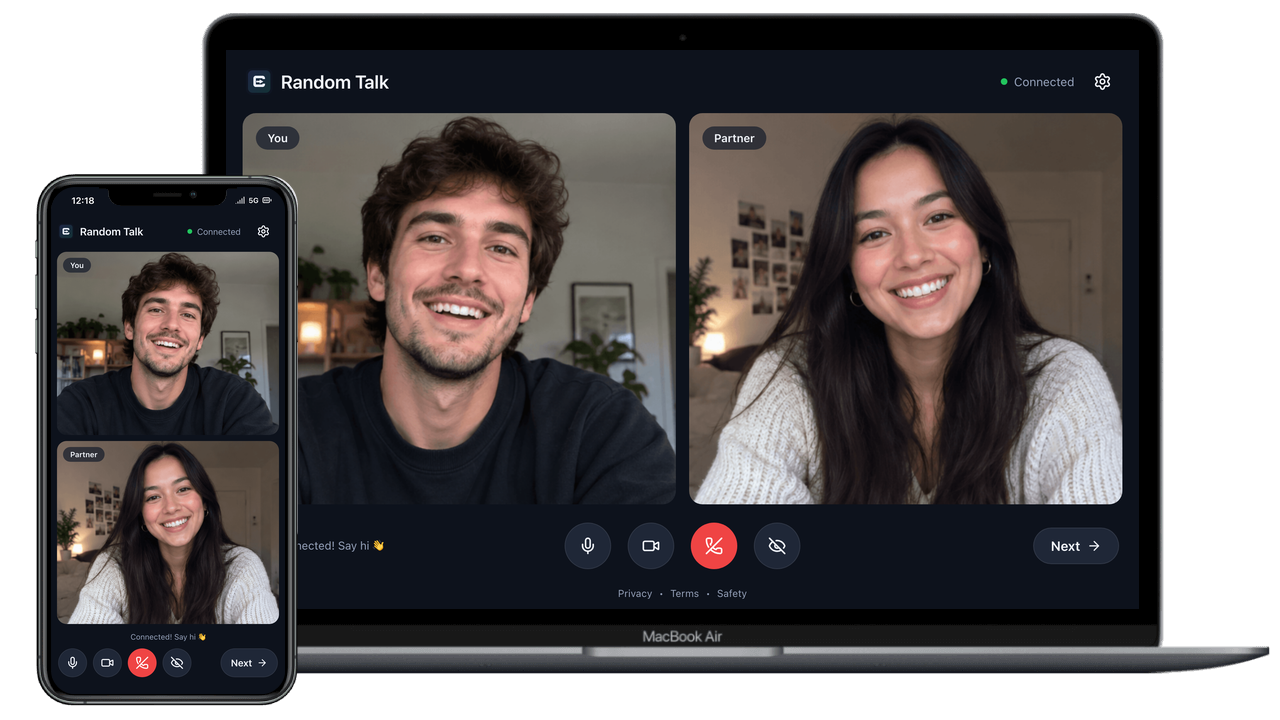
Description
MiroTalk RND is a self-hosted random peer-matching app for one-to-one WebRTC video chat.
Repository: miroslavpejic85/mirotalkrnd
Requirements
- OS: Ubuntu 22.04 LTS or 24.04 LTS (recommended)
- Node.js 24+ and npm (for local runtime)
- Docker Engine + Docker Compose v2 (for container runtime)
- Domain or subdomain with DNS
Arecord to your server (recommended for HTTPS) - TURN server for restrictive networks (STUN/TURN overview)
Automated setup
Quick Automated Installation
You can automate the entire setup (Node.js, Nginx, SSL, Docker) using our installation scripts on a clean Ubuntu server. Check out the MiroTalk RND Setup Script for details.
Quick start (Node.js)
Bash
# Clone the repository
git clone https://github.com/miroslavpejic85/mirotalkrnd.git

# Enter project folder
cd mirotalkrnd

# Copy environment template
cp .env.template .env

# Install dependencies from lockfile
npm ci

# Start server
npm start
Open: http://YOUR.DOMAIN.NAME:4010
Run with PM2
Bash
# Install PM2 globally
npm install -g pm2

# Start app
pm2 start server.js --name mirotalkrnd

# Persist process list and enable startup
pm2 save
pm2 startup
Run with Docker
Bash
# Clone repository
git clone https://github.com/miroslavpejic85/mirotalkrnd.git
cd mirotalkrnd

# Prepare env and compose files
cp .env.template .env
cp docker-compose.template.yml docker-compose.yml

# Pull image and start
docker compose pull
docker compose up -d
By default, RND listens on port 4010 (mapped from PORT in .env).
Automated installer (Ubuntu)
From the repository root:
Bash
sudo ./install.sh
The installer supports:
- Docker setup (official image
mirotalk/rnd:latestor local build) - Local Node.js setup
HTTPS reverse proxy (Nginx)
WebRTC camera/microphone permissions are most reliable on HTTPS in production.
Bash
sudo apt-get install -y nginx
Set your reverse proxy to forward traffic to http://localhost:4010 and terminate TLS with a trusted certificate (for example, with Certbot).
Next steps
- Review configuration options
- Expose local development safely with ngrok
- Estimate infrastructure with metrics guidance